What FloodCRM Is, How It Works, and Why It Matters
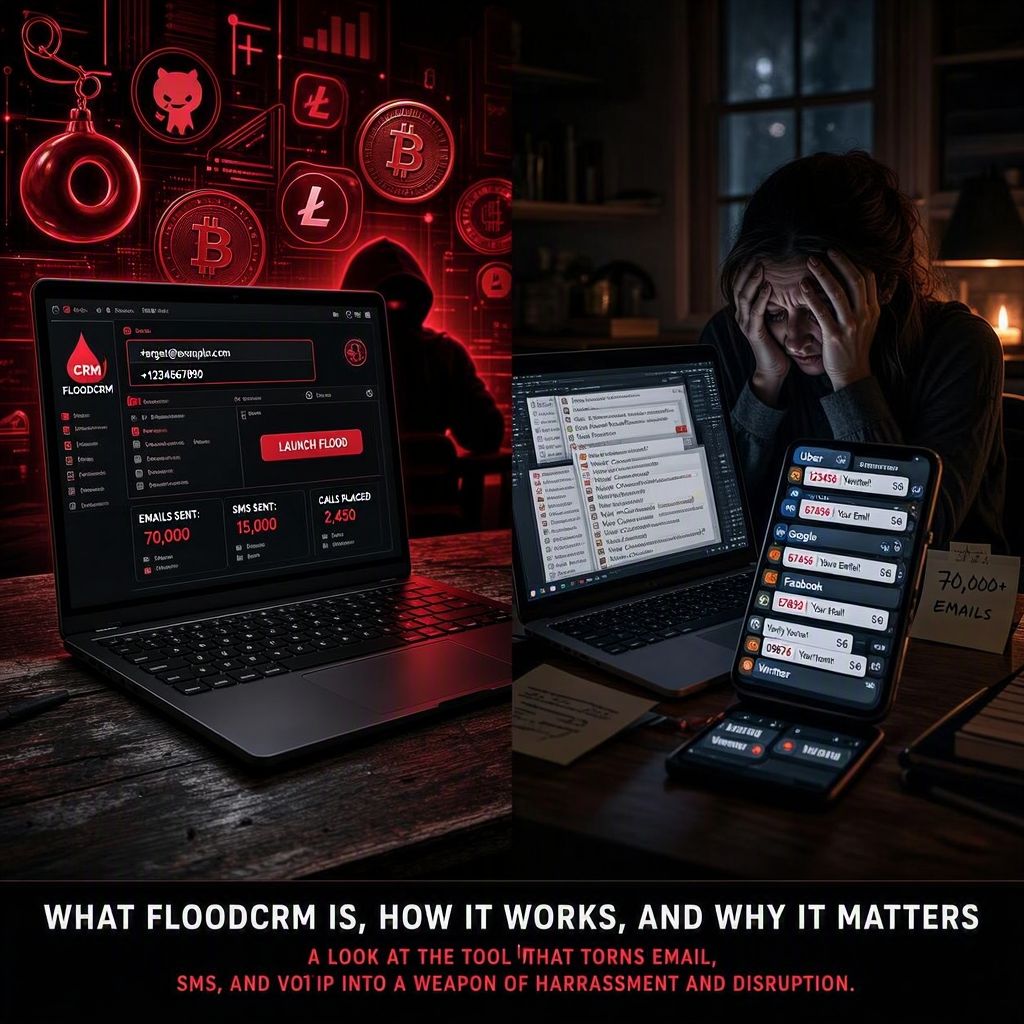
If you have spent any time in forums that discuss pranks, fraud prevention, or online harassment, you have probably seen the name FloodCRM come up. It is not a typical marketing tool. It is a platform built specifically for flooding someone's inbox and phone with so much noise that they cannot use them normally.
Understanding what it does, how it works, and why it is problematic matters whether you are researching the term out of curiosity or because you are on the receiving end of an attack.
What Exactly Is FloodCRM?
FloodCRM is a web based service that automates communication flooding. Think of it as a control panel that lets a user launch thousands of unwanted messages toward a single email address or phone number. It markets itself on scale and simplicity. You enter a target, pick a method, and the system does the rest.
Unlike legitimate outreach software that requires opt in lists and unsubscribe links, this type of tool is designed to overwhelm. That is the core reason it lives in a gray to black hat corner of the internet.
Since FloodCRM is invite-only, you can’t directly register by visiting their domain. Instead, you need to click on THIS CLEARWEB LINK or THIS ONION LINK if you’re using Tor. After registration, you can log in by visiting the link directly.
The Email Bomber Function
The email bomber part does not usually send emails directly from its own server. Instead, it exploits how many websites handle newsletters and account verification. FloodCRM takes the target email and automatically submits it to thousands of public subscription forms, forums, and free signup pages at once.
The result is that the inbox gets hit with a wall of legitimate confirmation emails, newsletters, and welcome messages. The platform claims it can trigger up to 70,000 of these in a single run. It is noisy, hard to filter at first, and it buries real messages.
The SMS Bomber Function
The SMS bomber works on a similar principle but for text messaging. Many apps and services send a one time password or verification code when you try to log in or register. FloodCRM automates requests to a long list of those services using the target phone number.
The person on the other end suddenly gets dozens or hundreds of OTP codes per minute from different brands. It does not hack the phone, it just makes the message app unusable and can cause the user to miss important codes.
The Phone Call Bomber Function
The phone call bomber feature is more aggressive. It uses VoIP systems to place repeated automated calls to the target number. Some versions play silence and hang up, others loop a prerecorded message. The goal is to tie up the line so real calls cannot get through and to force the person to put their phone on silent.
Why This Tool Blew Up In Certain Circles
Several things made FloodCRM stand out from older flooding scripts that you could find for free on GitHub.
First is volume. Sending tens of thousands of emails or texts manually would take forever. FloodCRM bundles it into one click and advertises numbers that free tools cannot match.
Second is access and privacy. It is an invite only service, which helps it stay under the radar and avoid being shut down quickly. It runs on both the regular web and through the Tor network, so users can reach it via its onion address. Payment is accepted in Bitcoin and Litecoin, which adds a layer of anonymity compared to PayPal or a credit card.
Third is cost. Compared to running your own botnet of accounts and proxies, a cheap subscription to a ready made flooder is appealing for people who do not have technical skills. That low barrier is why it has been linked to communities involved in carding, harassment, and other disruptive activity.
The Broader Picture
FloodCRM sits at the intersection of abuse, automation, and anonymity. Because it is accessible through both the clearnet and the Tor network, it is hard to take down permanently. Because it accepts cryptocurrency, it is hard to trace. And because it weaponizes ordinary signup forms and OTP flows, it is hard for victims to block at the source.
The tool also highlights a larger problem in the ecosystem. Legitimate websites that offer free signups, free newsletters, and free SMS verification become unwilling participants in every attack. They absorb the traffic, their deliverability scores drop, and their users get dragged into someone else's conflict.
The Legal And Practical Risks You Should Know
It is easy to think of flooding as just an annoying prank, but it is not treated that way legally. Using FloodCRM to target someone can fall under harassment, stalking, or computer misuse laws depending on your state. If it interferes with a business or emergency communications, the penalties get much more serious.
There are also practical risks for the person paying for it. Invite only flooders often log user data, even when they claim they do not. Paying with crypto does not make you untraceable if your login or email is linked to you. Many of these services are also scams that take your money and deliver very little.
From a platform perspective, all this traffic abuses legitimate websites. That is why most of the sites being abused will block the traffic, and why flooders stop working reliably after a while.
If You Are Getting Flooded, Here Is How To Handle It
If your inbox is suddenly flooded with subscriptions, do not try to unsubscribe one by one. Create a temporary filter in Gmail or Outlook for words like unsubscribe, newsletter, or verification and move them to a separate folder so you can still see real messages from contacts.
For SMS and call flooding, contact your carrier. Most major carriers can enable temporary call filtering or spam blocking at the network level. On your phone, turn on silence unknown callers for a day or two and let important calls go to voicemail. You can also use your phone's built in spam reporting to quiet the SMS side.
Document everything with screenshots and timestamps. If the flooding continues for more than a few hours or includes threats, file a report with local law enforcement and with the FBI Internet Crime Complaint Center. That documentation helps a lot if you need to pursue further action.
Final Thoughts
Tools like FloodCRM show how easy it has become to weaponize everyday systems like newsletter signups and OTP codes. The technology itself is simple automation, but the impact on a real person can be significant. If you are researching it for cybersecurity or educational reasons, focus on defense and awareness, not on using it against others.
Disclaimer: The details shared here are intended for educational purposes only. Using services like (FloodCRM)](https://floodcrm.org) for harmful or illegal activities is unethical and illegal. Always adhere to legal standards and ethical practices when engaging with digital communication tools.